Most AI-built apps ship with the same three holes. Database rules that let everyone in. Keys bundled into the website. Payments that believe anyone. Nobody checks, because nobody knows to.
of Lovable apps scanned by one researcher had broken or missing database rules, exposing emails, payment data and API keys.
CVE-2025-48757 ↗vulnerabilities and 400+ exposed secrets found across 5,600 public vibe-coded apps.
Escape.tech research ↗is when Gmail started rejecting mail from domains without proper authentication. Password resets and receipts can quietly disappear.
Gmail sender rules ↗Can customer B seecustomer A's data?
The first thing we check, and the most common failure. The policy below is what AI builders often generate. Switch the user and the policy to see what each customer can read.
TaskNest is a demo app we built with deliberate flaws to show what an audit finds. These results match the real tests in our sample report.
Everything that breaksafter launch.
We sign in as two unrelated customers and an anonymous visitor and try to reach each other's data. Then we read every rule, key and function. We find problems by testing, not by guessing.
Data access
Row-Level Security that really separates customers, not a policy that only says it does.
Secrets
Service keys and AI keys kept out of the browser and git, and rotated if they ever leaked.
Auth and admin
Roles users can't change themselves, and admin checks enforced on the server.
Payments
Verified Stripe webhooks, and plans that change only when money actually moved.
Files and privacy
Private storage, links that expire, and no customer list visible to every user.
Backups
Backups that are actually tested, and a restore plan for the day something goes wrong.
Performance
Indexes and queries that hold up at 100× today's data, measured on a staging copy.
SPF, DKIM and DMARC, so password resets and receipts land in the inbox.
Already ran your builder's security scan? Good.
Run it first. It's free and it catches the easy things. Here's what it can't see, in the platforms' own words: Lovable says its scans don't replace a professional review for apps with sensitive data.
| What gets checked | Built-in scannersLovable, Supabase, Bolt, Replit | Postlaunch audit |
|---|---|---|
| Tables with security switched off | Yes | Yes |
| Rules that let every signed-in user in | Yes | Yes |
| Two real customers trying to read each other's data | No. Lovable's paid pentest signs in as one user | Yes, with proof |
| Rules that exist but don't match your business | No. A scanner can't know who should see what | Yes |
| Payments: plans change only when money moved | Partly, in deep scans you run by hand | Yes, tested end to end |
| Backups that restore, monitoring, email setup | No | Yes |
| Each fix proven by re-running the test | No | Yes, plus a 90-day warranty |
Diagnosis first.Fixed price second.
Nothing is tested without your written permission, and nothing is fixed without a price you agreed to first.
Health call
We look at what any visitor can see, your public pages and email setup, and tell you what's worth worrying about.
Audit
You sign a one-page Authorization to Test. We test, then hand you a plain-English report with evidence and a fixed price for every fix.
Stabilize
We fix the top issues in your own repo, re-run every test and update your grades. You see the before and the after.
Care
Monitoring, updates and a monthly security re-check, so it stays fixed while you keep shipping with AI.
Fixed prices.No surprises.
Start small or go straight to the full audit. Every fix is quoted at a fixed price before any work begins.
Security Snapshot
For founders who want a quick, honest answer.
- Database rules tested with two users
- Secrets, auth and payment webhook
- 1-page risk summary and video walkthrough
- 2 days · credited to any fix
Production-Readiness Audit
For apps about to launch, raise, or take more payments.
- Everything in the Snapshot
- Performance, backups, deployment, email
- 10–15 page report with evidence
- Fixed-price fix plan and 30-min review
- One free re-test after your fixes
- 5 business days
Stabilize Sprint
We fix what the audit found, in your repo.
- Top 5–10 issues fixed
- Tests on critical paths
- Monitoring and backups set up
- Re-test and updated report
- 90-day warranty on every fix
- 1–3 weeks · 50% upfront
Care Plan
Keep it fixed while you keep shipping.
- Uptime and error monitoring
- Dependency and security updates
- Monthly security re-check and report
- 2 hrs of changes (Growth: $590, 6 hrs)
- Cancel anytime
Two guarantees. If the Production-Readiness Audit doesn't find at least 3 issues worth fixing, you get a full refund. And every fix we ship is under warranty for 90 days: if it breaks, we fix it free.
Supabase change fix
From 30 October, new tables in existing Supabase projects are no longer reachable from your app until they're granted access. When your AI builder adds a table, that feature fails with "permission denied". We check every table, add the right grants and security rules without opening your data to everyone, and test it as two users.
White-label audits
Building client apps on Lovable, Bolt, Bubble or Replit? We audit them before handover, under your brand, at partner rates. Your client gets the report with your name on it; you get a security partner on call.
See exactlywhat you get.
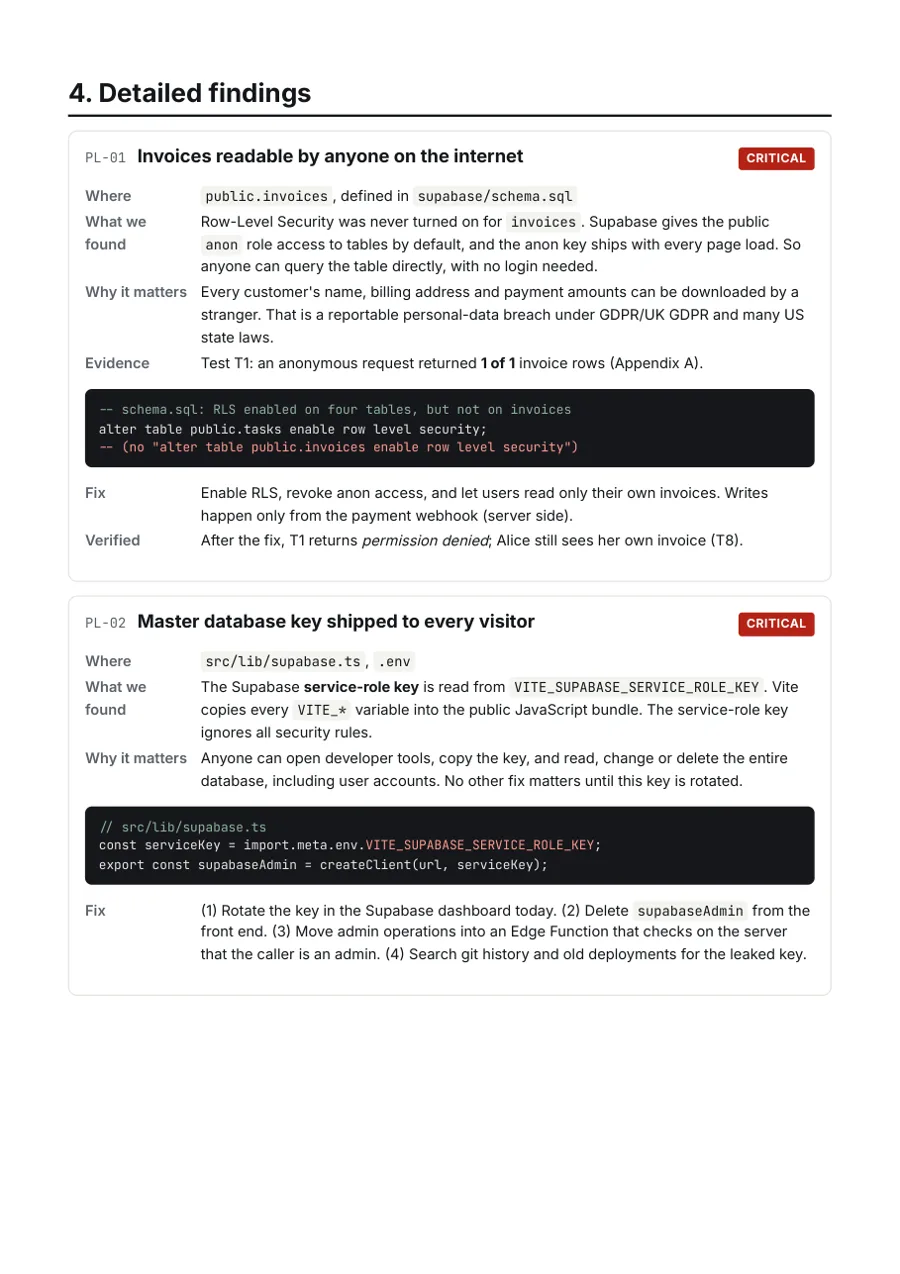
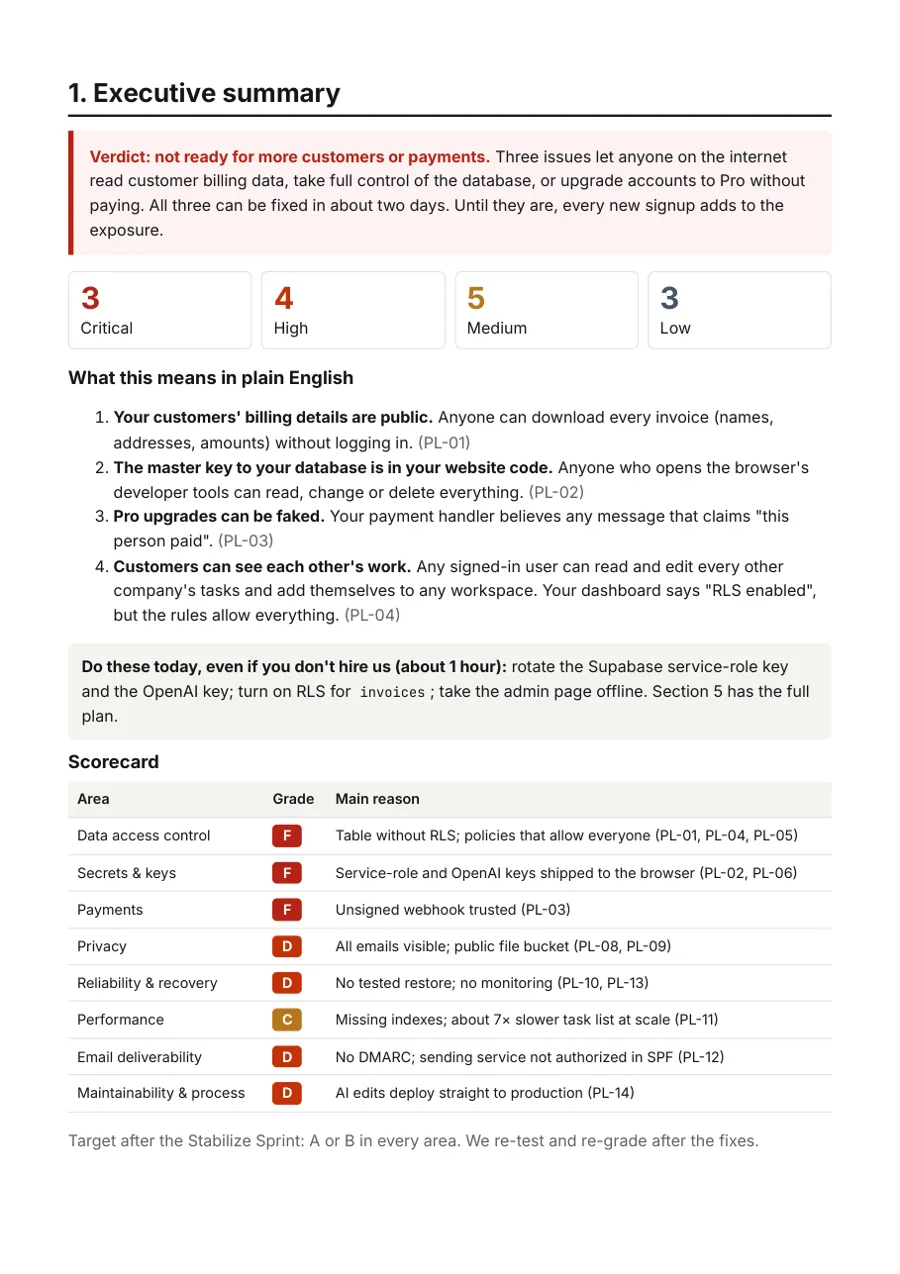
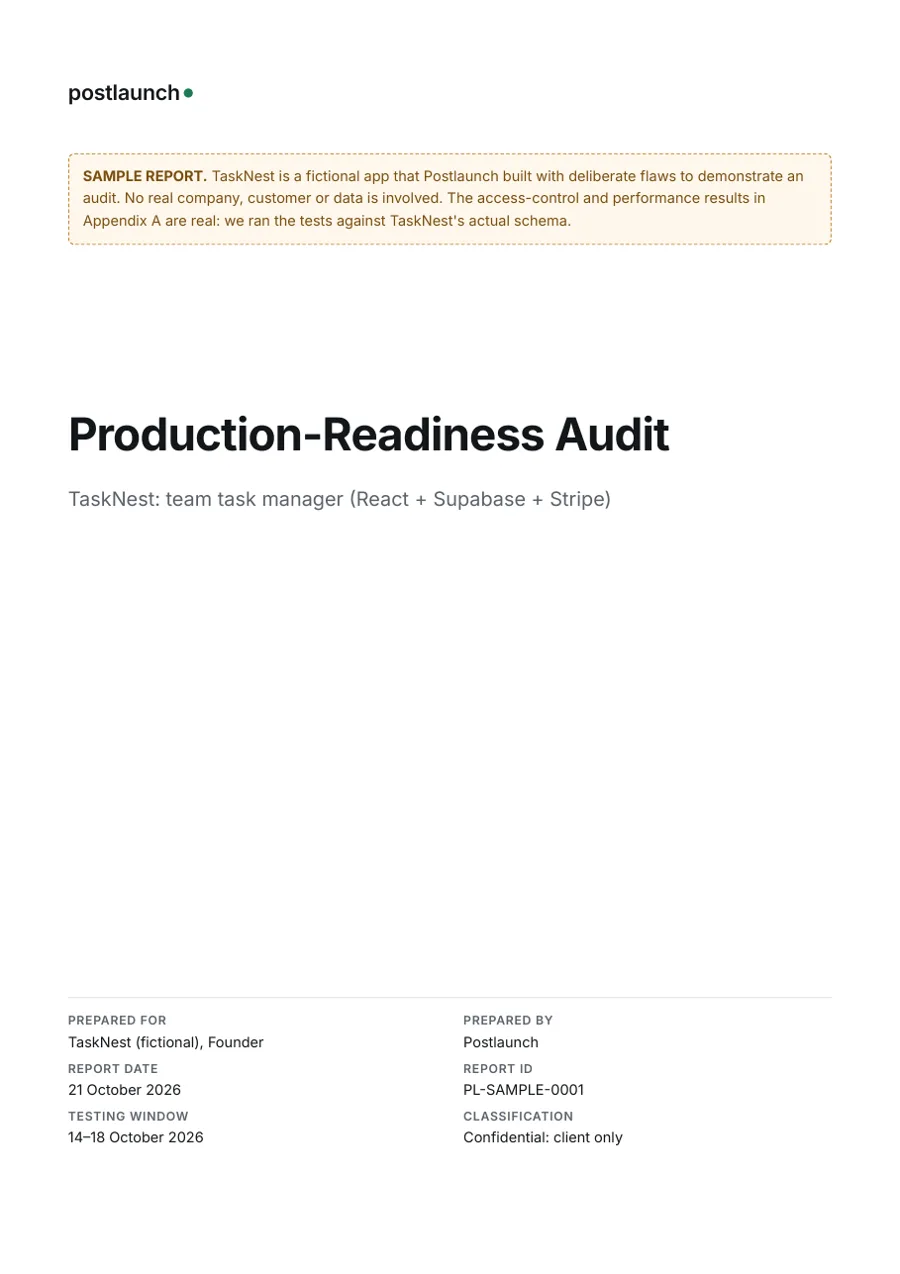
We built TaskNest, a typical React + Supabase + Stripe app, planted the mistakes AI builders commonly make, and audited it the way we audit client apps.
| We tried… | Before | After |
|---|---|---|
| Anonymous visitor reads invoices | 1 row | Denied |
| Customer B reads A's tasks | 2 rows | 0 rows |
| User makes themselves admin + Pro | Allowed | Denied |
| Task list at 1,000,000 tasks | 104 ms | 14 ms |
Checklist also in français.
Are your emailsgoing to spam?
Check your domain's email authentication. It reads public DNS records only, nothing is stored, and it works for any business, not just apps.
Plain English.Proof for everything.
Evidence, not opinions
Every finding says where it is, what can go wrong, and how we proved it. You can re-run our tests yourself.
Permission first
We only test apps we've been authorized in writing to test, within a named scope and window. It's a one-page form.
No judgement
AI builders are a brilliant way to start. We finish the job. We never mock the code, or the founder.
You own everything
Your repo, your accounts, your keys. Fixes arrive as reviewed changes you can apply with us or without us.
Questionsfounders ask.
Lovable (or Bolt, or Supabase) already has a security scanner. Why do I need this?
Run it first: it's free and catches missing rules. But scanners check that rules exist, not that they work for your business, and Lovable's own docs recommend a professional review for apps with sensitive data. We test your app the way a second customer or a stranger would, then read the code to explain why. See the comparison.
Can't I just ask the AI to fix it?
For small things, yes. The issues that hurt are cross-cutting: who can see what, where keys live, what proves a payment happened. The AI can't flag them because it doesn't know what's supposed to be private. The audit tells you, and then the AI (or we) can fix it.
Will you break my live app?
No. Testing uses dedicated test accounts and a staging copy wherever possible. Fixes go to staging first, get re-tested, and only then go live. We never load-test production.
What access do you need? Is my code safe?
Read access to your repository and a read-only view of your backend dashboard, granted and revoked by you. Before testing, you sign a one-page authorization naming exactly what we may test. NDA on request. You own all code and documents we produce.
Which stacks do you work with?
Mostly React/Vite and Next.js front ends on Supabase or Firebase, with Stripe, Vercel or Netlify and Resend or Postmark: the usual output of Lovable, Bolt, v0, Replit and Cursor. Bubble apps too. Not sure if yours fits? Ask on the free call.
Where are you based, and how do we work together?
We work remotely with founders in the US, UK, EU and Australia. You get written updates, a video walkthrough of every deliverable, and replies within one business day. Calls are scheduled to overlap with your working hours.
Find out what's reallygoing on in your app.
No testing without your permission. You'll leave knowing what to fix first, whether or not you hire us.